
NERC CIP
COMpLIANCE
How do you make sure Cyber Security and Compliance are perfectly aligned?
Scroll to find out.
Scroll to find out.
Often, our clients
end up with stacked responsibilities:
1
The ones which make the grid run safely, reliably, and securely
2
The ones which keep the regulators from fining them
The secret sauce is aligning the stuff that makes the grid safe and secure with the stuff that makes the auditors happy.
That’s how you get Compliance Through Security as opposed to the other way around. It’s what makes security folk's day jobs better, easier, faster, and even fun.
That’s how you get Compliance Through Security as opposed to the other way around. It’s what makes security folk's day jobs better, easier, faster, and even fun.
Program
Development
CIP Program need polishing? Fresh blueprints? Tear down renovation?
Hit us up.
Hit us up.
Gap Analysis
Find gaps. Action plan. Close gaps.
It’s that simple.
It’s that simple.
RSAW/ERT
Development
RSAWs aren’t evidence. They’re context. They tell your compliance story.
In contrast, your CIP Evidence Request Tool = actual evidence.
Let us help you package your audit submittals, from narratives to performance records.
In contrast, your CIP Evidence Request Tool = actual evidence.
Let us help you package your audit submittals, from narratives to performance records.
Audit Preparation
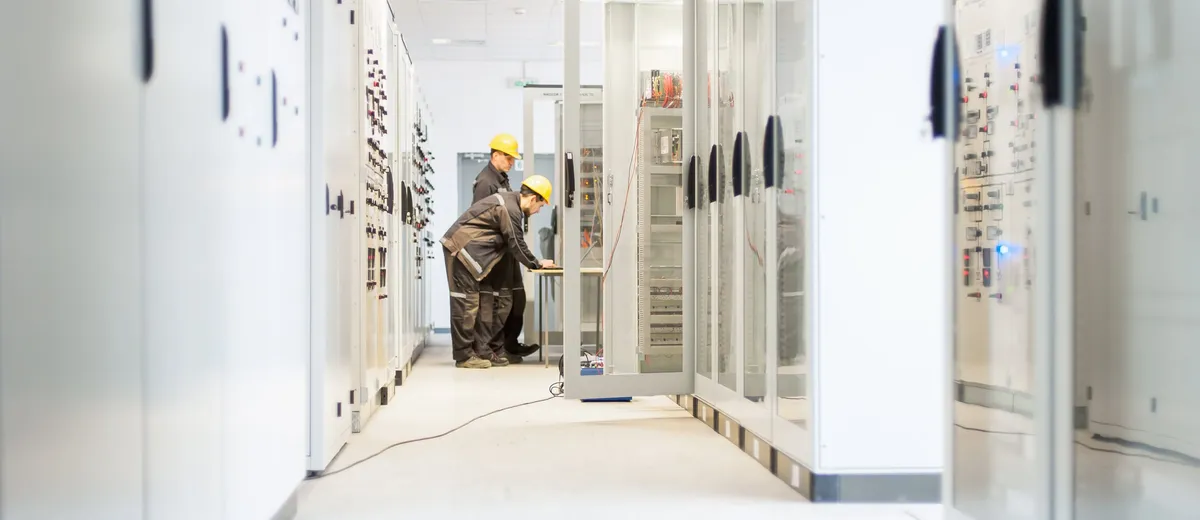
We have RSAWs in our blood. We have NERC ERT data requests in our hearts. We dream about SME interviews. Don’t hit the panic button...we’ll get you ready for your CIP Audit.
Mock Audit
Simulate the real thing. Practice makes perfect. We’re tough but fair.
We love to put our auditor hats on, and we've sat on both sides of hundreds of audit tables.
We love to put our auditor hats on, and we've sat on both sides of hundreds of audit tables.
Remediation Services
Auditors find problems...we can fix them. But don't wait until the audit.
ESP getting sloppy? We’ll clean that drawing right up. Firewall rulesets a mess? Let’s get those justifications nailed down.
We can start eliminating bottlenecks, clarifying roles and responsibilities, and improving evidence quality right now.
ESP getting sloppy? We’ll clean that drawing right up. Firewall rulesets a mess? Let’s get those justifications nailed down.
We can start eliminating bottlenecks, clarifying roles and responsibilities, and improving evidence quality right now.
Vulnerability
Assessment
CIP-005. CIP-007. CIP-010.
Paper / Active VAs.
Medium / High Impact.
10 devices to 10,000 devices.
Let’s go!
Paper / Active VAs.
Medium / High Impact.
10 devices to 10,000 devices.
Let’s go!
CIP-013
Supply Chain
CIP-013 doesn’t have to be your unlucky number. We’ve built dozens of CIP-013 programs and counting.
Better yet, we support procurement teams as they’re learning the NERC CIP ropes.
Sustainable, repeatable, compliant, and secure. That's Supply Chain Risk Management.
Better yet, we support procurement teams as they’re learning the NERC CIP ropes.
Sustainable, repeatable, compliant, and secure. That's Supply Chain Risk Management.
Internal
Controls
Not required? More work? Unrewarded?
How about: reduces stress, simplifies reporting, and saves time.
Compliance looks backwards at past performance. Internal Controls look forwards to your program's future.
Learn to love them...our clients do (and so do the auditors!).
How about: reduces stress, simplifies reporting, and saves time.
Compliance looks backwards at past performance. Internal Controls look forwards to your program's future.
Learn to love them...our clients do (and so do the auditors!).
Tabletop Exercise
Affordable, quick, and highly effective way to see how your team would handle surprises in a real-time simulation of a cyber security incident. Custom injects and scenarios to keep things interesting. Reporting and cleanup for any findings. Lessons learned for compliance.
Check your CIP-008 IRP Drill off your compliance to-do list every year with us!
Check your CIP-008 IRP Drill off your compliance to-do list every year with us!
Technical
Documentation
Your CIP documents have to be more than just a restatement of the standards - they have to have some local flavor (i.e. match the look and feel of your organization) and they have to clearly explain why you’re doing it, what needs to get done, who's going to do it, and how SMEs are going to generate performance records that prove compliance...every time!
Training
CIP 101 ("Uhhh...what’s a NERC?") through CIP 400 ("Yes, I have the evidence right here" and other magic words used by NST's Wizards of CIP to nail audits) and everything in between.
Meaningful education for the compliance executive in her corner office suite, and for the tech junkie running cables around a substation, and even for the power engineer cleaning grease off his hands so he won’t get fingerprints all over his laptop.
Meaningful education for the compliance executive in her corner office suite, and for the tech junkie running cables around a substation, and even for the power engineer cleaning grease off his hands so he won’t get fingerprints all over his laptop.

